// Microsoft Security & Cloud — field notes
Security, straight from the field.
Deep dives on Defender XDR, Microsoft Sentinel and cloud security — written by Microsoft MVP Dominik Höfling.
11 posts7 topicslast update 2026-08-06
All posts
10 moreFrom MVP to Microsoft and Back Again: My Return to the Security MVP Community
I've been awarded Microsoft MVP status again, this time in Security with a focus on cloud security. A look back at the journey and what comes next.
Predictive Shielding in Microsoft Defender XDR: Moving from Disruption to Anticipation
Predictive Shielding in Defender XDR anticipates the attacker's next move and proactively cuts attack paths, building on Automatic Attack Disruption.
Mastering Microsoft Defender for Servers: Understanding P1 vs P2 and Choosing the Right Plan
Defender for Servers Plan 1 vs. Plan 2: capability differences, P1 subplan configuration, direct onboarding without Azure Arc, and when to pick which.
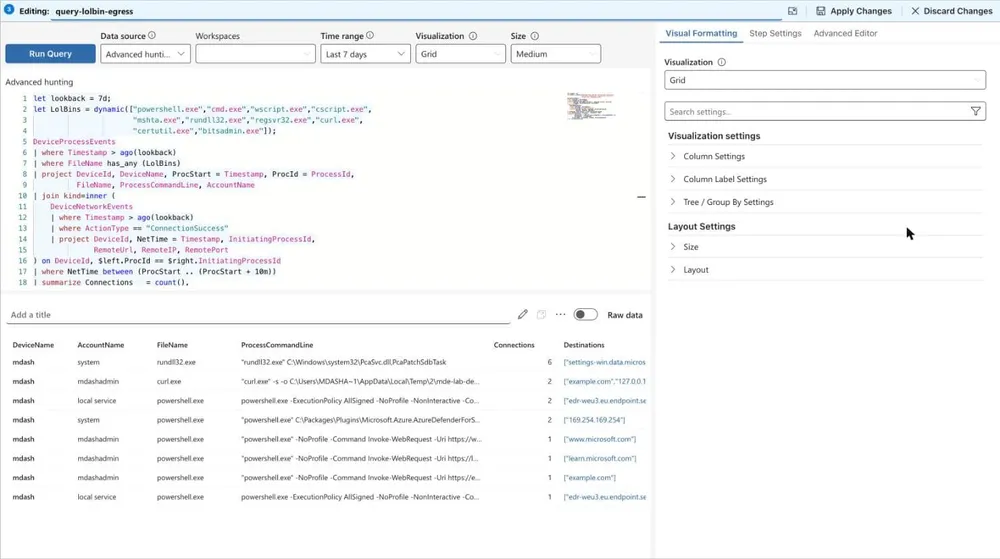
Advanced Hunting Across Microsoft 365 Defender and Sentinel
Why siloed defenses miss chained attacks, and how advanced hunting across Microsoft Defender XDR and Microsoft Sentinel closes the gaps.
Closing the Loop: How to Use Alert Feedback in Microsoft Defender for Cloud
Defender for Cloud's alert feedback is more than input for Microsoft. Capture it and your SOC can track alert quality, workload and tuning needs.
Why a SIEM Needs a Data Lake: The Case of Microsoft Sentinel
Why does a SIEM need a data lake? What the Sentinel Data Lake changes for scalability, cost and long-term retention of security data.
Defender for Office 365 Dual Use / Defense In-Depth
Which Defender for Office 365 features you get depends on where your MX record points. An overview for setups with a third-party email filter.
Mastering Multi-Tenant Security: Microsoft Sentinel Strategies for Distributed and Centralized Setups
Distributed, centralized or hybrid: how MSPs and enterprises design Microsoft Sentinel across multiple tenants, with tools for cross-tenant visibility.
Exchange Online Security Best Practices – 10 Tips From The Field
Ten field-tested security tips for Exchange Online: MFA and blocking legacy auth, SPF, DKIM and DMARC, Safe Links and Safe Attachments, CAE and more.
Exchange Hybrid Security Best Practices – 7 Tips From The Field
Seven field-tested security tips for Exchange Hybrid: harden Entra ID Connect, set up SPF, DKIM and DMARC, point MX to EOP, keep servers patched.
// who writes this
Dominik Höfling
Cloud security architect and Microsoft MVP with 15+ years across Azure, AWS and Microsoft 365. Author and speaker focused on XDR, CNAPP and SIEM.